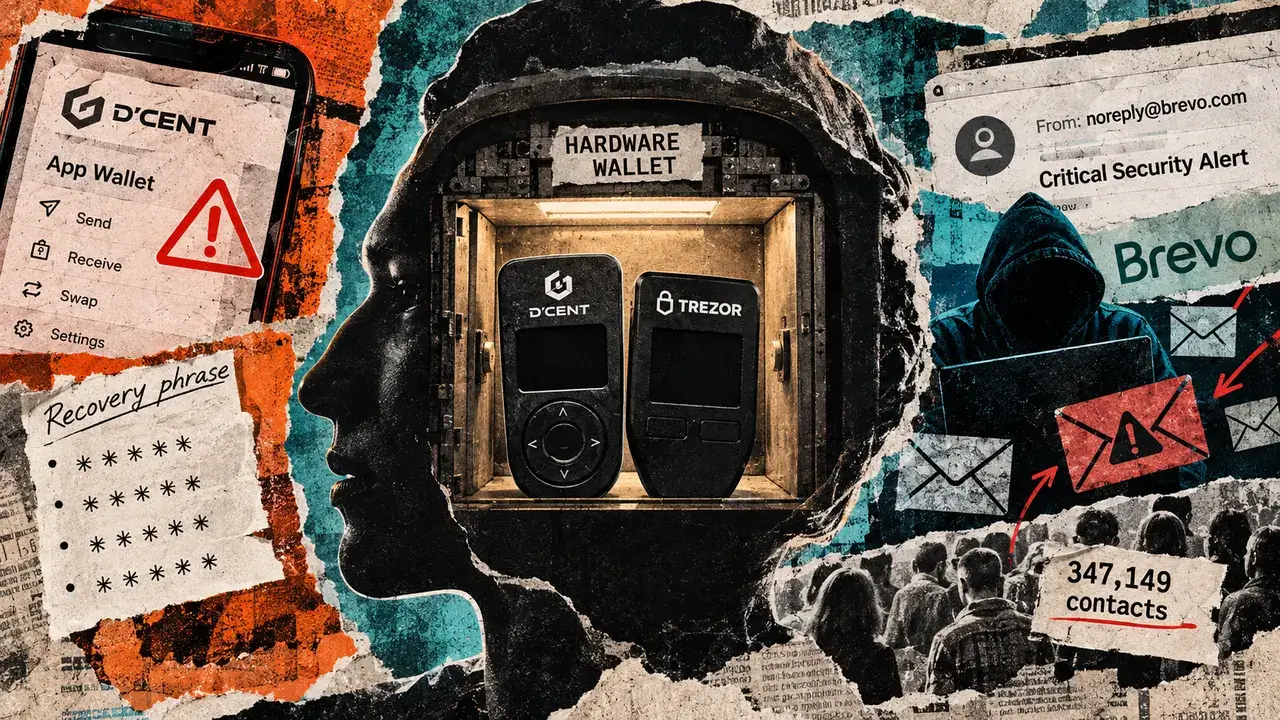
Hardware wallet security remains robust in 2026 despite a series of high-profile software-signing and vendor-data failures that targeted the crypto industry early this year. These failures do not compromise the actual private keys stored on physical devices, as the 'secure element' chips are architecturally isolated from the internet and the host computer's software. Even if a vendor's update server is breached and a malicious firmware update is pushed, the device’s internal logic prevents the extraction of the seed phrase, provided the user does not manually input their recovery words into a phishing interface.
The context for these concerns involves a major January 2026 breach where multiple wallet providers saw their software-signing certificates compromised, leading to legitimate-looking but malicious prompts on desktop applications. For US-based investors, this serves as a critical reminder that self-custody is a multi-layered process. The failure of vendor data—such as email addresses or shipping info—poses a physical privacy risk, but the cryptographic integrity of the Bitcoin or Ethereum held on the device stays intact as long as the physical verification steps are followed correctly.
From a regulatory perspective, the US Treasury's 2026 'Self-Custody Standards' report has highlighted these supply chain vulnerabilities as a reason to push for more transparent open-source firmware. While regulators are using these incidents to argue for stricter oversight of 'unhosted' wallet manufacturers, the market has interpreted the resilience of the hardware itself as a bullish sign for long-term asset safety. The fact that billions in assets remained untouched during a vendor-level failure reinforces the narrative that decentralized storage is superior to centralized exchange custody.
Looking ahead, investors should monitor the upcoming US House Financial Services Committee hearing on the 'Hardware Security Act of 2026,' which aims to standardize how manufacturers handle software-signing protocols. Users are advised to adopt multi-signature (Multi-Sig) setups, which provide an additional layer of protection by requiring approvals from multiple hardware devices, effectively neutralizing the risk of a single vendor's software supply chain failure.