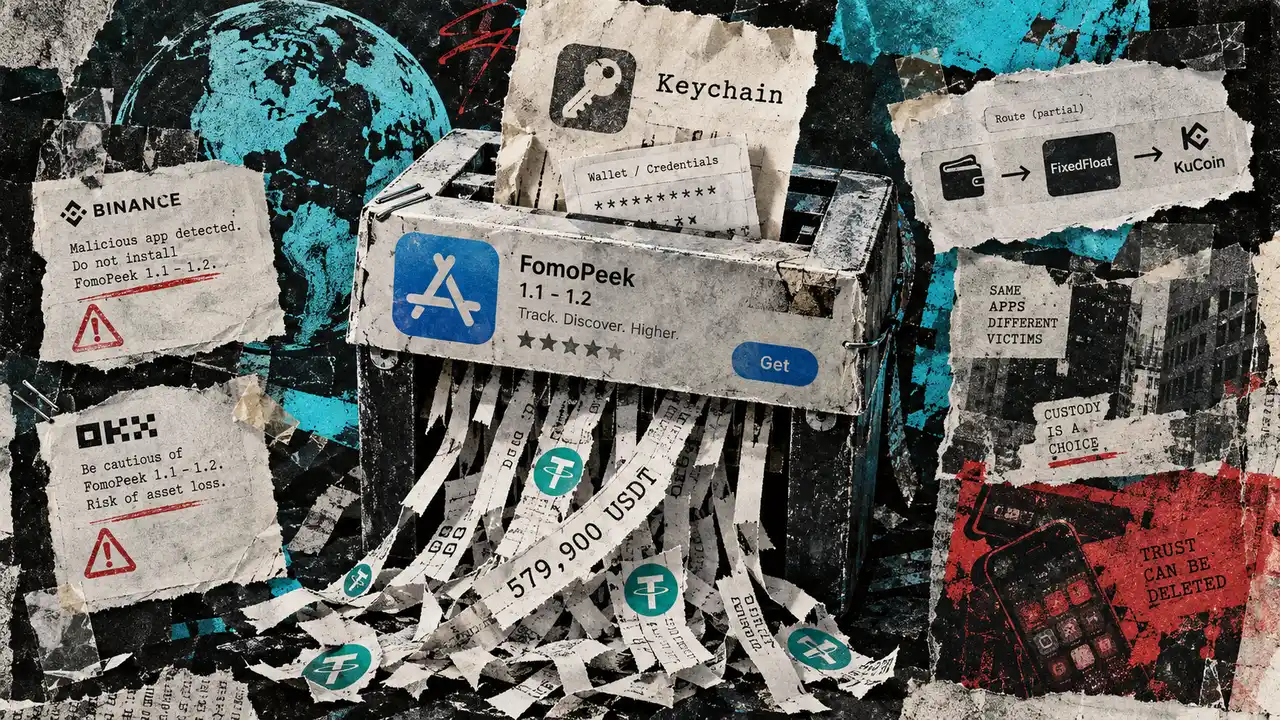
The Fomopeek application managed to steal nearly $580,000 in Tether (USDT) by successfully bypassing the iOS sandbox security layer to hijack users’ private keys. This critical breach allowed the malicious software to move assets directly from victims' wallets without their authorization. According to reports from blockchain security firm SlowMist, the theft is specifically linked to versions 1.1 and 1.2 of the app, which were distributed through Apple’s official App Store before being identified as rogue.
SlowMist launched a comprehensive investigation after receiving multiple reports of assets being drained from mobile wallets over the weekend. Their findings highlight a significant vulnerability in how the app interacted with system-level data. While the App Store is generally considered a 'walled garden' with high security standards, this exploit proves that sophisticated malware can still slip through Apple’s review process, specifically targeting the exposed private keys of mobile crypto users.
The theft of $580,000 is a significant blow to mobile security sentiment in the US crypto market. As more retail investors rely on smartphones for DeFi interactions and daily payments, the ability for a rogue app to escape its sandbox environment raises questions about the fundamental safety of mobile hot wallets. This event could trigger renewed calls from US regulators for Apple to implement more stringent vetting processes for financial and blockchain-related software.
Investors are urged to check their device history and immediately delete any instance of the Fomopeek app. Security experts recommend moving funds to new, hardware-backed wallet addresses to mitigate the risks posed by sandbox-escaping malware. As the investigation continues, the industry will be watching closely for a formal response from Apple regarding their security patch timeline and any updates from SlowMist on the flow of the stolen funds.