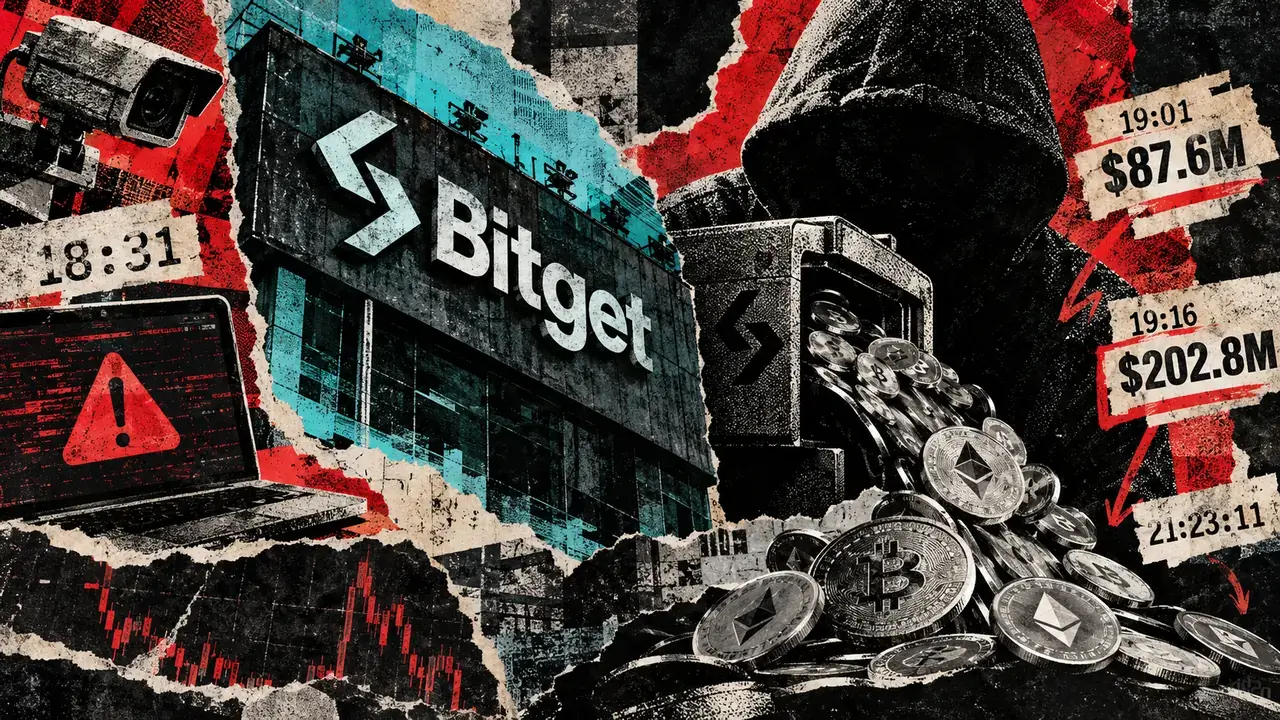
Bitget exchange had approximately 30 minutes to respond to a detected intrusion before hackers began moving roughly $290 million in stolen assets. According to data provided by blockchain security firm Hypernative, the first significant wave of unauthorized transfers was initiated 30 minutes after Bitget reported its initial detection, with a second wave following at the 45-minute mark. This narrow timeframe underscores the extreme speed required for exchange security teams to mitigate damage during high-stakes exploits in the current 2026 digital asset landscape.
The incident has reignited debates regarding the efficacy of centralized exchange (CEX) emergency protocols and automated circuit breakers. While Bitget's monitoring systems successfully identified the breach, the delay in freezing the affected wallets or suspending outgoing transactions allowed the attackers to move a significant portion of the funds. Hypernative’s analysis suggests that the sheer volume of the $290 million transfer indicates a sophisticated, multi-vector attack that targeted specific liquidity pools, potentially overwhelming the platform's immediate manual intervention measures.
From a regulatory perspective, this breach is expected to draw scrutiny from U.S. authorities who have been pushing for more robust consumer protection standards for offshore exchanges. The event highlights a recurring vulnerability in the global crypto infrastructure: the gap between detection and mitigation. As the industry moves further into 2026, regulators are increasingly looking at whether exchanges should be mandated to have pre-authorized 'kill switches' that can be triggered by third-party security audits when massive, unauthorized outflows are detected.
For the broader crypto market, the Bitget exploit has caused localized volatility and intensified the push for users to move assets into self-custody or hardware-backed solutions. Investors should watch for an official post-mortem from Bitget regarding the status of their 'Protection Fund' and whether it will be sufficient to cover the $290 million loss without impacting exchange operations. The focus now shifts to whether advanced AI-driven security firms can provide faster response times to prevent these massive outflows before they reach decentralized mixers and cross-chain bridges.