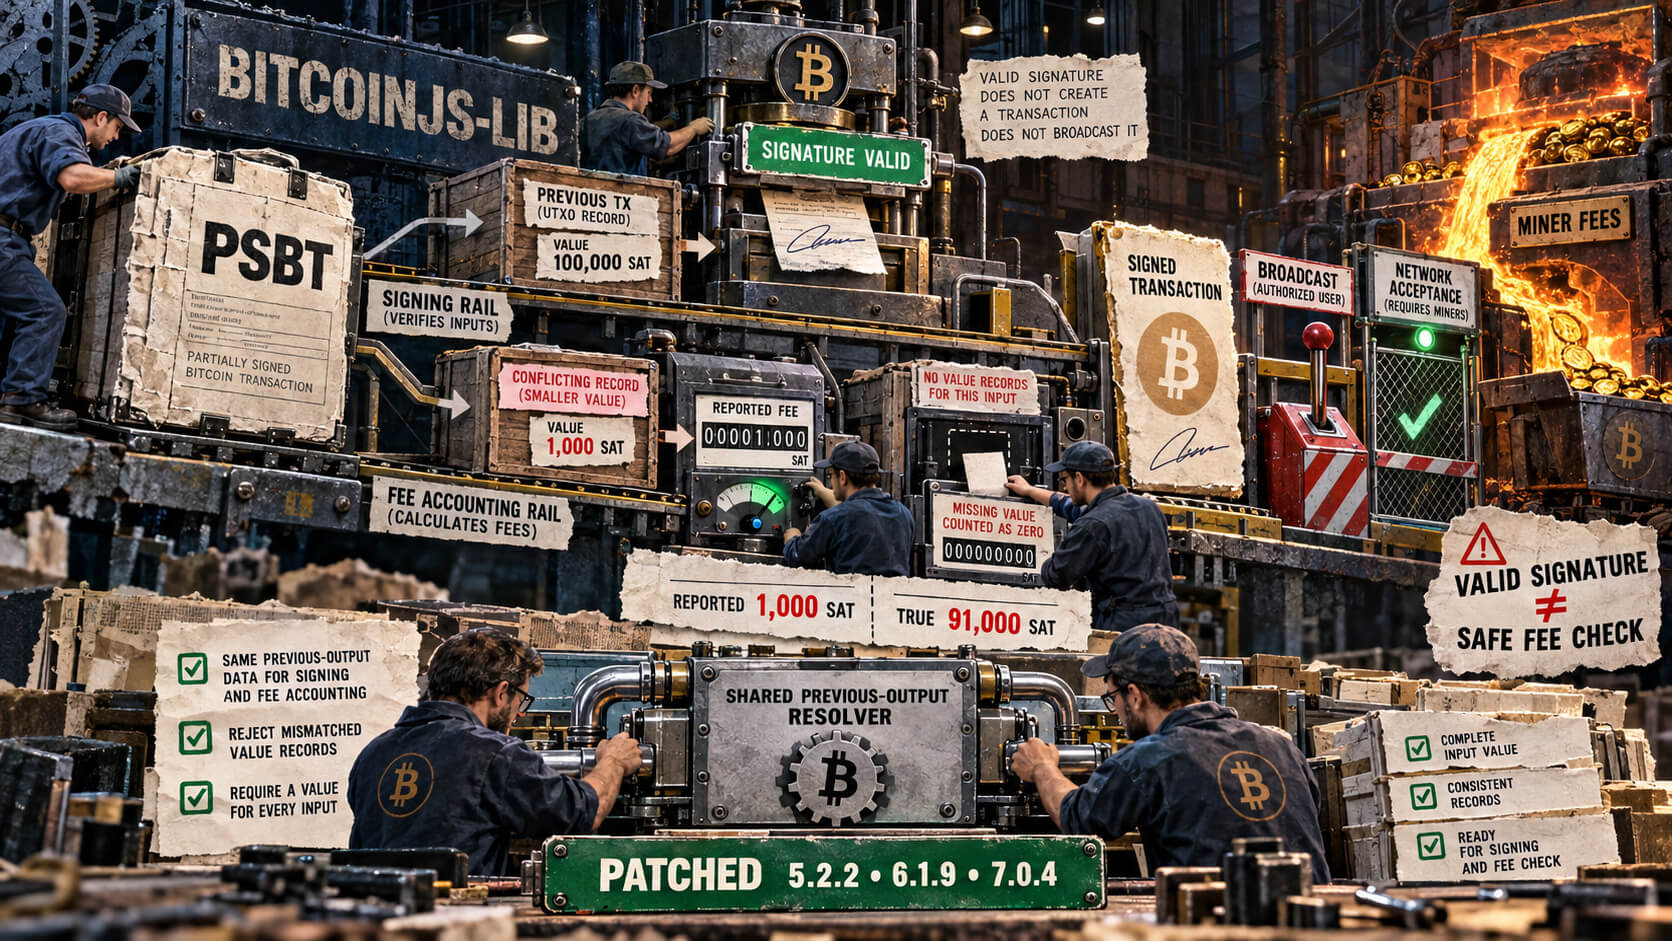
The Bitcoin PSBT library vulnerabilities lead to excessive fee drains by tricking wallet software into miscounting the total value of inputs and outputs during the transaction signing process. When an application imports a compromised or malformed PSBT, the library's faulty accounting logic fails to recognize that the difference between the inputs and outputs—which constitutes the miner fee—is higher than intended. This flaw allows transactions to proceed without triggering the standard 'excessive fee' alerts that usually protect users from costly errors.
Technically, these bugs affect the way third-party applications parse transaction data before signing. Because the library misreports the fee amount to the user interface, a user might believe they are paying a standard network fee while the actual transaction structure allocates a much larger sum to miners. This type of 'fee-sniping' risk is particularly dangerous for automated systems and hardware wallet integrations that rely on these libraries to validate transaction integrity before final authorization.
In the current 2026 regulatory environment, US-based crypto service providers are under increased pressure to demonstrate robust supply chain security. This discovery highlights the ongoing risks associated with shared code dependencies in the Bitcoin ecosystem. Security researchers suggest that these vulnerabilities could be exploited by malicious actors to craft specific transaction requests that quietly siphon funds from institutional hot wallets or retail multi-sig setups, making it a high-priority fix for infrastructure providers.
Market participants should watch for emergency patches from major wallet providers and library maintainers. If your Bitcoin service provider utilizes PSBTs for multi-device signing, ensure that their backend libraries have been audited against these specific accounting bugs. The industry is now moving toward mandatory redundant verification steps, where the wallet hardware must independently calculate fees regardless of what the software library reports, to mitigate these 'blind signing' risks.